
AI does the prep. Your auditors own the opinion.
Trenta checks the evidence before it tests a control, runs the test steps, and cites every conclusion to its file. Your team reviews and signs.
Running live SOC 1, SOC 2, ISO 27001, PCI DSS and NIST CSF engagements.
Evidence first. Then the test. Then your sign-off.
Before an AI agent tests a control, it should check whether the evidence can support a conclusion at all. Trenta works in that order.
Check the evidence
Agents read the artifacts from your drive or GRC tool and validate client reports and populations for completeness and accuracy. Gaps are flagged before any testing starts.
Run the test
Agents run the test steps and record results in your firm's own workpaper templates, in the right tabs and cells, with each conclusion cited to its evidence file.
You review and sign
Every agent action is logged with its inputs, reasoning and references, so your reviewers can trace any conclusion back to the file. The judgment and the opinion stay with your team.
Hundreds of testing procedures. Every conclusion cited to its file.
A Report on Compliance carries hundreds of testing procedures, each one needing documented evidence and a defensible observation. Trenta assembles the report with every conclusion tied to the evidence that supports it, then cross-checks the report against notes and evidence before partner review.
RGP's QSA practice is running PCI DSS engagements on Trenta.
Report generation. Audit reports and PCI ROCs assembled from the tested work.
Consistency checks. Drift between the report, the notes and the evidence is flagged before a partner sees it.
Complete audit trail. Inputs, outputs, reasoning, timestamps and references for each agent action.
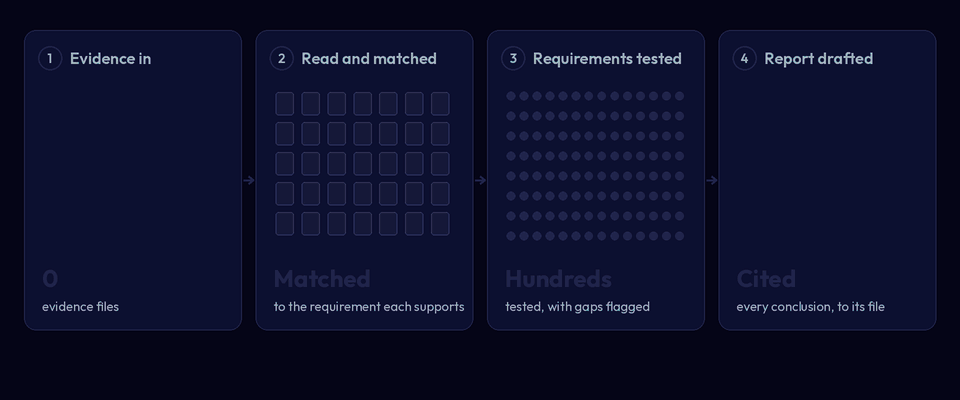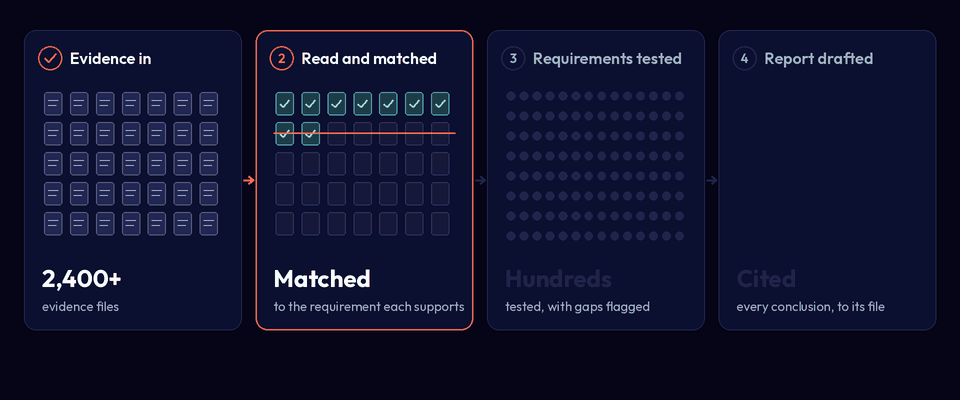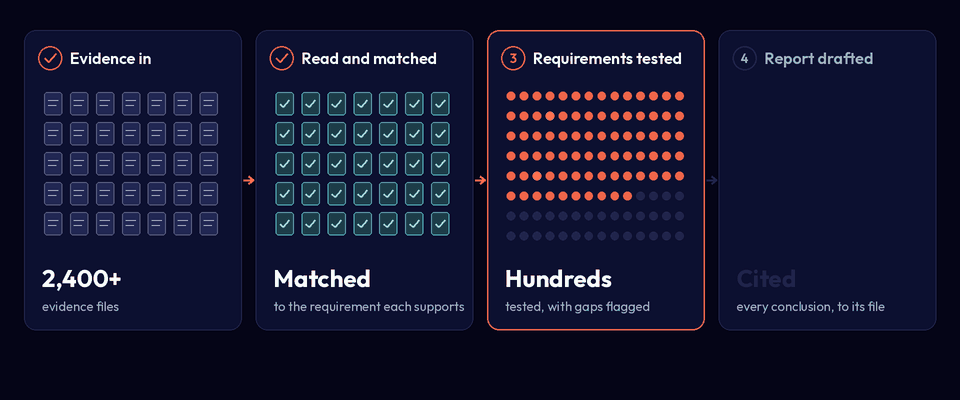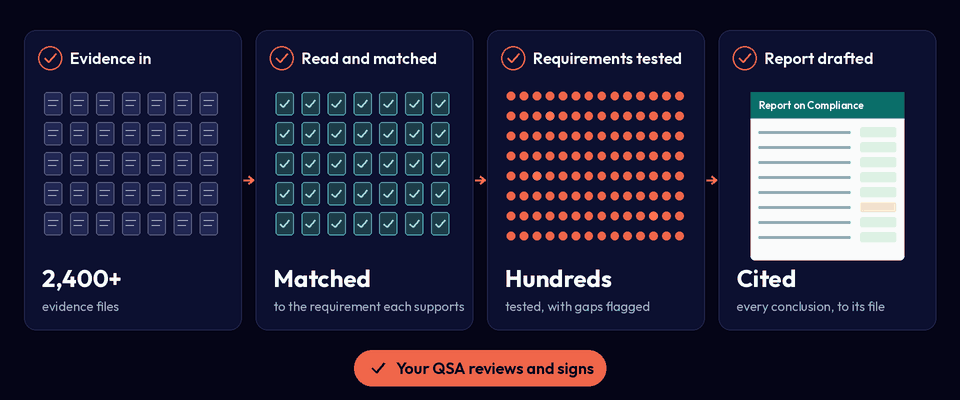
From client evidence to a signed workpaper.
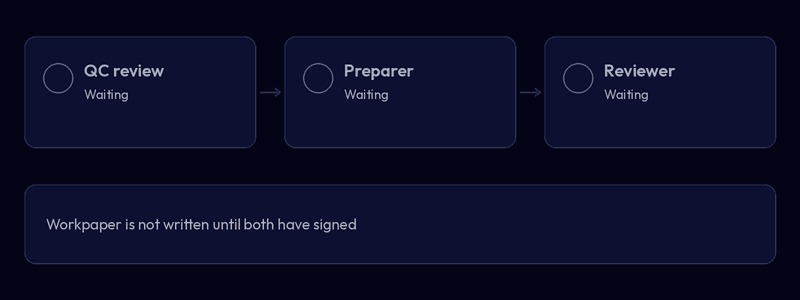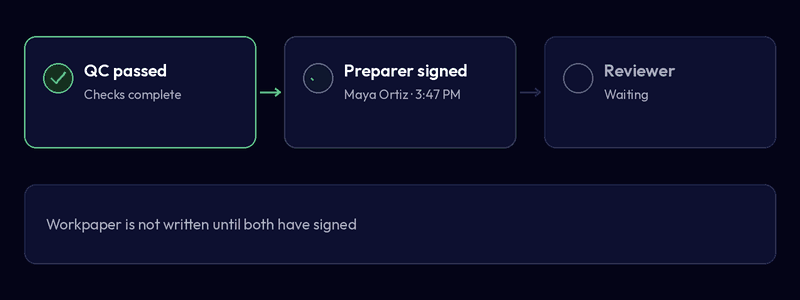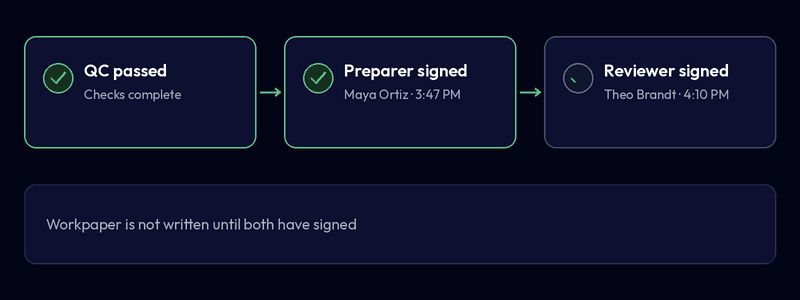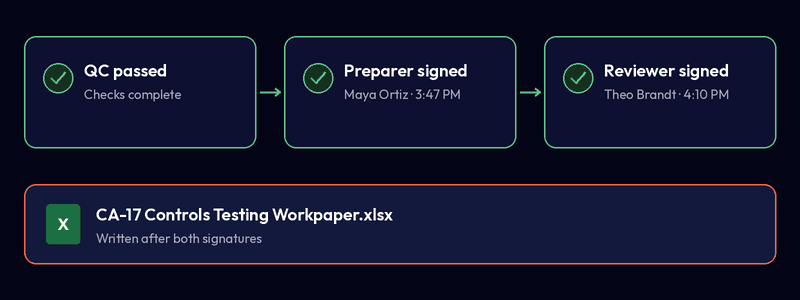
Trenta runs SOC 2 controls testing with auditor checkpoints built in. Nothing reaches the workpaper unsigned.
Your evidence, where it already lives
Controls, descriptions and evidence come in from Vanta and Suralink, already matched to the controls they support.
Evidence checked before it is tested
Completeness and accuracy are checked on the population before a sample is drawn. Evidence that falls short goes to follow-up, not to a conclusion.
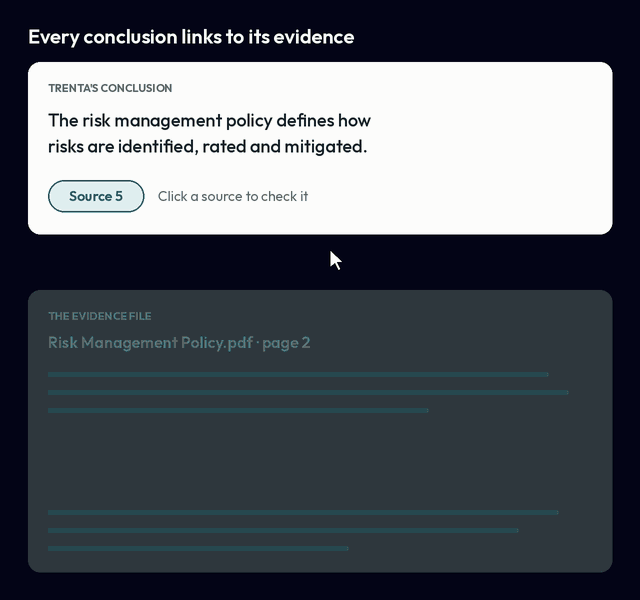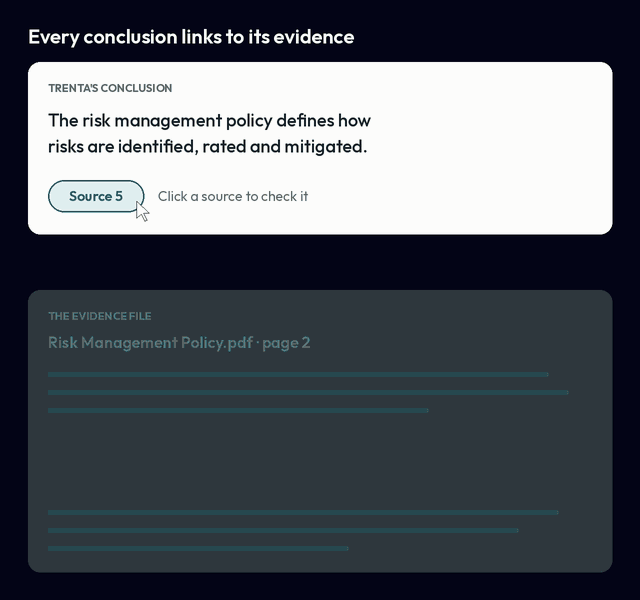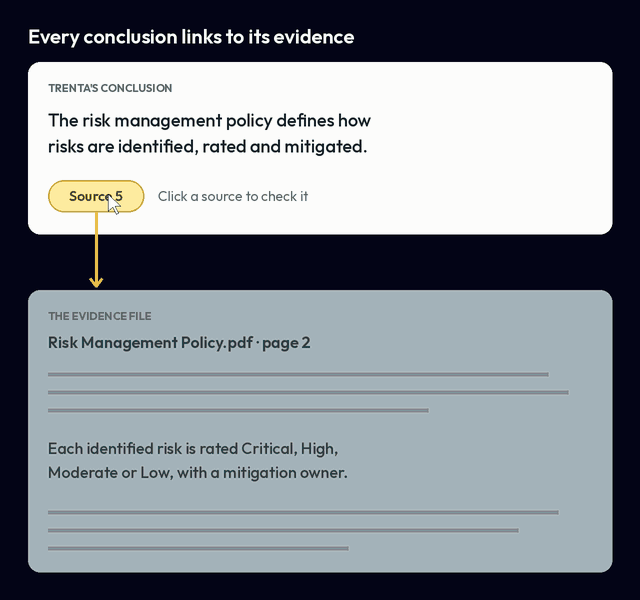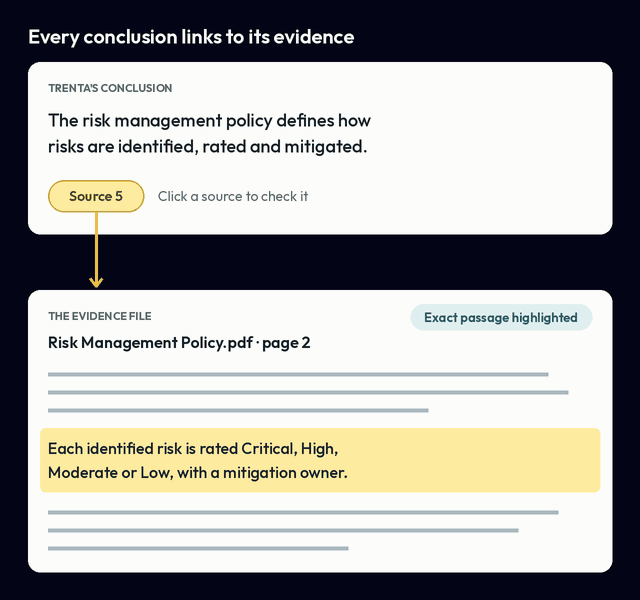
Every conclusion resolved to its source
Click a citation and land on the highlighted passage in the original document.
The AI prepares. You sign.
A preparer and a reviewer sign independently before any workpaper is written.
A workpaper, not a chat log
Each control ends with a real Excel workpaper and a Word verification report.
Internal audits and gap assessments, from first file to issued report.
One engagement covers the clauses, Annex A and the Statement of Applicability, with your reviewers deciding every grade.
Start from the Statement of Applicability
Import the client’s file. Checks flag missing reasons and gaps before any testing starts.
A proposed grade for each requirement
Each one comes with its evidence and rationale. A named reviewer accepts or adjusts it.
Findings in one register
Nonconformities and observations collect in a single log as they are accepted.
A report that waits for review
The report issues only after the quality review is complete.
Assessments that are scored and explained.
Trenta proposes a score for each subcategory and shows what it rests on. Every call stays with your team.
Collect
Import the client’s files. Each one links to its request item.
Set up
Set scope, profile and owners. Interview packets and questionnaires are drafted for you.
Score
Each subcategory gets a proposed score with its basis and confidence.
Review
Accept, adjust with a reason, or mark not assessed.
Report
Set targets, read the gaps, and export the report, deck and workbook.
They switched in the middle of busy season.
Nobody changes audit tools halfway through busy season, unless the new way is clearly better. SAV Associates did, moving to Trenta while already using another audit tool.
No template migration
Trenta fills your firm's existing multi-tab templates in place. Your workpapers keep their format.
Your tools stay the same
It works with Excel, Google Sheets, Google Drive, OneDrive and GRC tools such as Vanta, alongside what your team already uses.
It does the work
Trenta performs the tests and fills the reports, where other tools stop at recommendations.
SAV Associates sees AI as the future of audit, and Trenta as a leader in building AI-enabled tools for the IT audit industry.
Signed in October 2026, in the middle of busy season.
What audit leaders are saying.
After decades managing IT audits, I’ve seen how manual processes create bottlenecks that compromise both speed and quality. AI-powered solutions like Trenta’s approach could revolutionize audit work for HIPAA, ISO, SOC 2 and other frameworks, enabling auditors to complete engagements faster while maintaining the high accuracy standards our clients expect.
Cybersecurity consulting is drowning in manual document review and evidence collection. AI that can automatically identify supporting evidence, generate a list of potential compliance gaps, and flag risks across HIPAA, ISO, and other frameworks is transformative - allowing consultants to focus on strategic advisory work rather than sifting through the details.
The audit and advisory industry desperately needs AI solutions that automate repetitive compliance tasks while preserving critical thinking. Trenta’s approach to building specialized audit intelligence could transform how we deliver strategic value to clients, freeing us from administrative overhead to focus on high-impact advisory work.
Frameworks in live engagements
See it on your own engagement.
A 30-minute walkthrough with the Trenta team, using your framework and your workpaper format.